
Fix WordPress Email Delivery With SMTP (Step by Step)
WordPress emails vanish because PHP mail() isn't authenticated. Route them through a real SMTP server, with fallback relays and a log, so they arrive.
You build a contact form. Someone fills it in. The email never arrives—or it shows up in spam, or three hours late. Then a customer never gets their password reset, and you find out weeks later. Silent email failure is one of the most common WordPress problems I get called about, and the cause is almost always the same, boring, fixable thing. Here’s why it happens and how to fix it for good in about five minutes.
The essentials
- WordPress’s default
mail()is unauthenticated, so Gmail, Outlook and Yahoo treat it as spam. - Since February 2024, Google and Yahoo require SPF or DKIM from every sender, and both plus DMARC above 5,000 messages a day—unauthenticated mail may be filed as spam or rejected (Google’s sender guidelines, Yahoo’s).
- The SMTP Mailer has presets for 12 providers (Brevo, SendGrid, Mailgun, Amazon SES, Postmark, Gmail, Outlook, Zoho and more) plus a custom option—pick one and host/port/encryption fill in.
- Its standout feature is fallback relays in priority order: if the primary provider fails, the next takes over automatically.
- It can log every send, lets you test each relay and check your sender domain’s SPF, DKIM and DMARC records, imports from WP Mail SMTP / Post SMTP / Easy WP SMTP, and can alert you by email or a Slack, Discord or Teams webhook on failure.
Why do WordPress emails fail by default?
WordPress emails fail by default because PHP’s mail() sends them straight from your web server, with no SPF record authorizing it, no DKIM signature and no sending reputation. Since February 2024, Gmail and Yahoo require SPF or DKIM from every sender, so an unauthenticated WordPress site lands in spam or gets rejected.
WordPress sends mail through PHP’s mail() function, which fires messages directly from your web server with no authentication. There’s no SPF record vouching that your server may send for your domain, no DKIM signature proving the message wasn’t tampered with, and no established sending reputation behind the IP.
To inbox providers, that profile is indistinguishable from spam—because that’s how most spam is actually sent. So your legitimate password resets and contact-form notifications get filtered, delayed, or dropped without a bounce.
It got stricter recently. Since February 2024, Google and Yahoo require every sender to authenticate with SPF or DKIM, and senders of more than 5,000 messages a day to have both plus a DMARC policy (Google, Yahoo). An unauthenticated WordPress site isn’t just likely to land in spam anymore—Gmail may reject the message outright. Authenticated SMTP isn’t a nice-to-have; it’s the baseline.
Most delivery problems trace back to one of a handful of causes—here’s how each maps to the fix:
| Symptom | Cause | Fix |
|---|---|---|
| Emails never arrive, or land in spam | PHP mail() is unauthenticated—no SPF, DKIM or reputation | Route mail through an authenticated SMTP server |
| Can’t reach Gmail or Yahoo at all | Since February 2024 they require SPF or DKIM from every sender | Add the SPF and DKIM records your provider gives you |
| SMTP set up, still going to spam | The From address doesn’t match your authenticated domain | Set the relay’s From Email to an address on that domain |
| Mail dies when the provider is down | A single relay with no backup | Configure fallback relays in priority order |
How do you configure SMTP in WordPress?
To fix WordPress email delivery, stop relying on PHP’s mail() and route messages through an authenticated SMTP server instead. In Blaminhor Essentials, activate the SMTP Mailer module and work through four short steps: pick a provider preset, add fallback relays, send a test and check your sender domain, then turn on the delivery log with failure alerts.
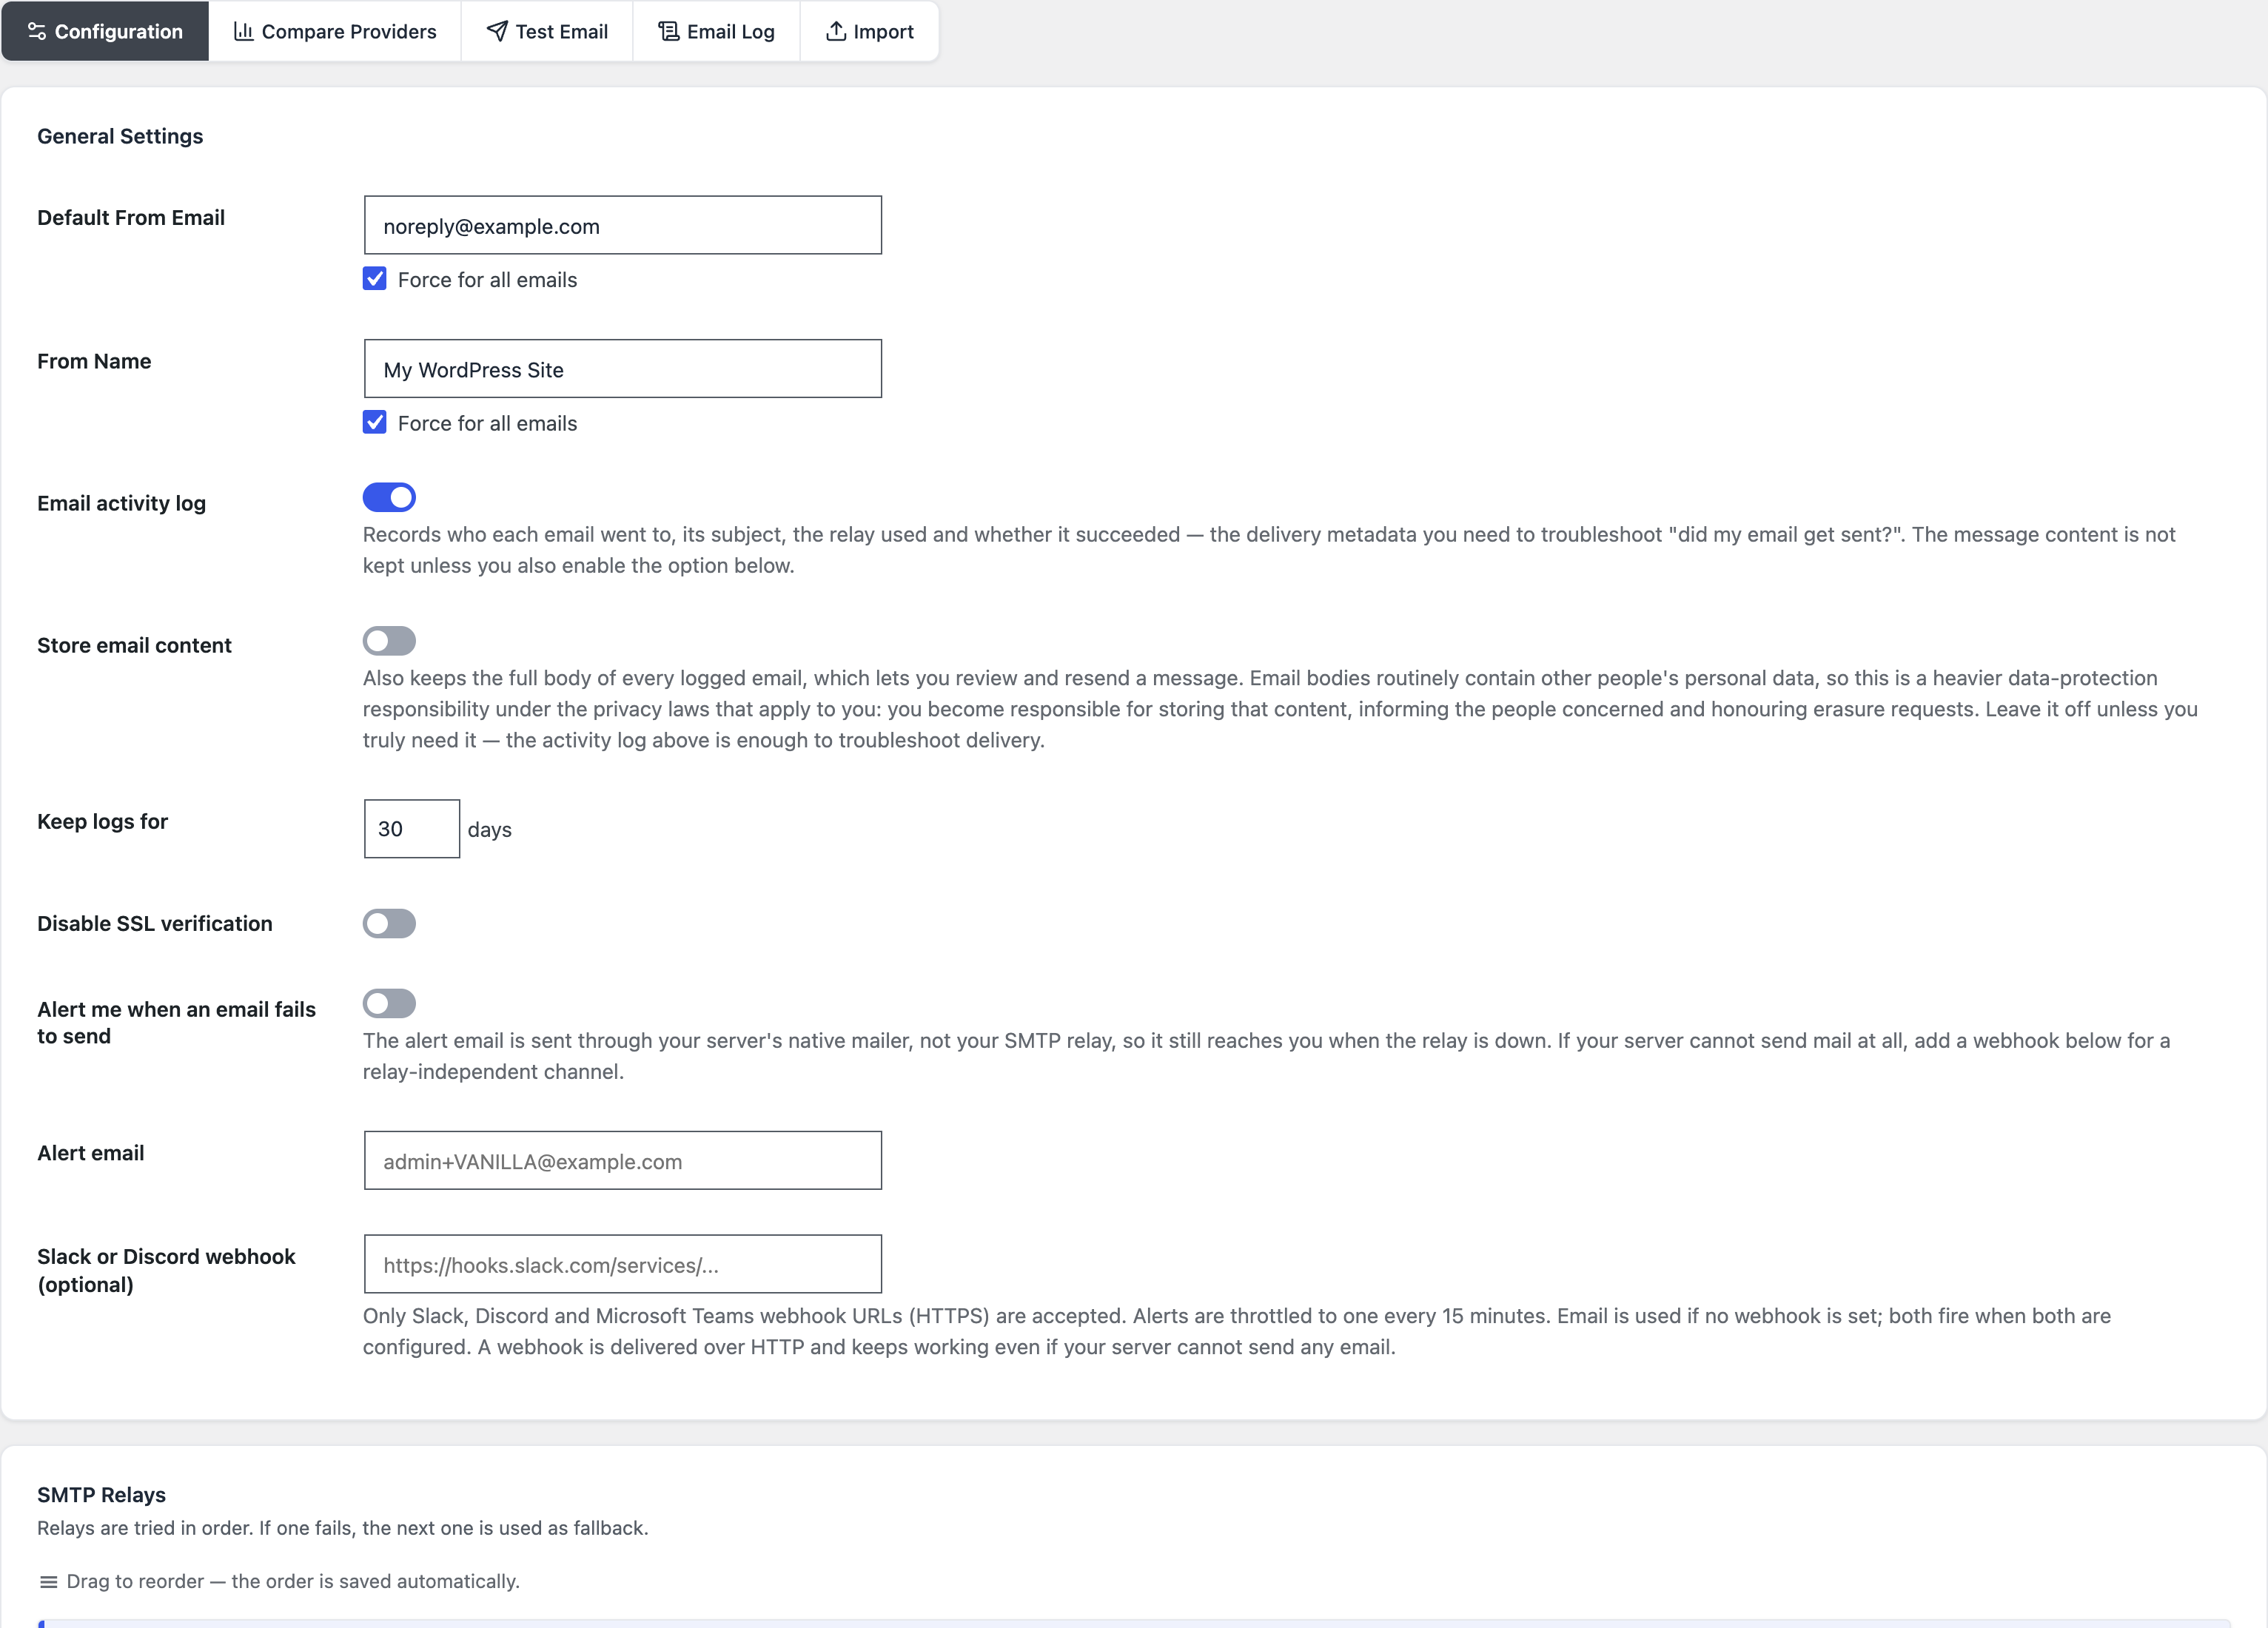 The Configuration tab: sender defaults, the email activity log and failure alerts above, the relays tried in order below.
Step 1 — Choose a provider
The module ships presets for 12 providers: Brevo, SendGrid, Mailgun, Amazon SES, Postmark, SparkPost, Mailjet, SMTP2GO, Elastic Email, Gmail / Google Workspace, Outlook / Office 365 and Zoho Mail—plus a custom option for anything else. Pick yours and the host, port and encryption (TLS) are filled in automatically; you add your credentials (an API key or username/password) and the relay’s From Email, the address your emails will be sent from. If you don’t have a provider yet, a free-tier transactional service like Brevo is a fine place to start: the Brevo setup, DNS records included, is walked through step by step.
Step 2 — Add fallback relays
This is what sets the module apart from most SMTP plugins. You can configure several relays in priority order. If the primary one fails—server down, quota reached, authentication rejected—the module automatically retries through the next, with an internal guard so a failing fallback can’t loop back on itself. Your password resets and form notifications still go out even when a provider is having a bad day.
Step 3 — Test it and check your domain
Send a test email through your primary relay, or test each relay on its own with its Test button. A test never falls back to the next relay, so it shows exactly what that relay answered. On failure, the result shows you the exact server error; and once the delivery log is on, its Relay column tells you which relay delivered each message—so “did that send?” stops being a guess.
Next to Test, each relay also has a Check domain button (since version 2.7.3). It reads your sender domain’s DNS and tells you whether the SPF record authorizes your provider, whether a DKIM key is published (for providers that use one fixed selector, such as Brevo) and whether a DMARC policy exists. A relay never reports any of that: a provider like Brevo can accept a message and drop it afterwards when the sender domain isn’t authenticated on the account.
Step 4 — Monitor delivery
Turn on the email log and every message is recorded: subject, recipient, status, which relay sent it, and timestamp. Logs auto-purge after a retention window (30 days by default), and you can optionally log message content for deeper debugging. When a send fails, enable failure alerts to be notified by email or a Slack, Discord or Teams webhook (at most one alert every 15 minutes; the alert email goes out through your server’s own mailer, not the failing relay)—so you catch a delivery outage in minutes, not when a customer complains.
Why are my WordPress emails not sending, and can a failed one be retried?
WordPress emails that “don’t send” were either refused by your mail server or provider, or delivered and then filtered as spam, and the delivery log shows which. When every relay refuses an email, the SMTP Mailer can keep an encrypted copy and retry it up to 5 times within 72 hours.
A failed status with the server’s error means a configuration or provider problem: credentials, quota, an outage. A sent status with nothing in the inbox points to spam filtering and your DNS records, which the email deliverability guide covers.
That retry queue is on by default and still labelled Beta. As of version 2.8.6, it works like this:
- Up to 5 attempts, about 5 minutes, 35 minutes, 2 h 35, 14 h 35 and 62 h 35 after the failure.
- 72 hours at most: the copy is deleted once the email is sent, once the fifth attempt fails, or after 72 hours at the latest.
- 500 emails at most, and 2 MB of attachments per email.
- Encrypted on your server, listed in a Retry queue tab, and you can switch the feature off, which deletes whatever is waiting.
So a short provider outage no longer has to mean lost emails: the queue retries them on that schedule, and, if you turned on failure alerts, an alert tells you it happened.
How do you migrate from WP Mail SMTP, Post SMTP or Easy WP SMTP?
Only the password needs re-entering. If you already run WP Mail SMTP, Post SMTP or Easy WP SMTP, the SMTP Mailer module’s Import tab copies their SMTP server settings into a new relay, switched off (passwords are never imported, for security); add the password, switch the relay on, and you’re done, rather than a re-setup.
Which other options are worth knowing?
Two settings on the Configuration tab are worth a look: the default From Email and From Name, used when a relay has none of its own, and Disable SSL verification, meant for local development only. Everything else—host, port, encryption—comes from the provider preset, so there is little left to tune by hand.
- Default From Email / From Name — each relay already sends from its own From Email, so nothing slips out with a mismatched address; the “Force for all emails” box next to From Name sets the sender name for plugins that set their own, when the relay has no From Name.
- Disable SSL verification — for local development with self-signed certificates only; never on production.
What changes once SMTP is in place?
Emails that arrive—in the inbox, not in spam, and not three hours late. And if one provider stumbles, a fallback relay quietly picks up the slack and, with failure alerts on, you hear about it. It’s five minutes of setup against weeks of silent, invisible failures.
While you’re tidying up WordPress email, it’s worth stopping the automatic notifications you don’t want so only the mail that matters goes out, and the email log is where you go the day someone says “I never got it.”
SMTP Mailer is one of the 26 modules in Blaminhor Essentials—free and open-source on WordPress.org.
– blaminhor
FAQ
Do I need SPF and DKIM records for WordPress email?
Yes. Since February 2024, Google and Yahoo require every sender to authenticate with SPF or DKIM, and both plus a DMARC policy above 5,000 messages a day; unauthenticated mail may be filed as spam or rejected. A reputable SMTP provider gives you the records to add to your domain's DNS, which is what makes delivery reliable.
Can I use my Gmail account to send WordPress emails via SMTP?
Yes. You can route WordPress mail through Gmail or Google Workspace using their SMTP server, and the SMTP Mailer module ships a Gmail preset for exactly that. It works well at low volume, but Google enforces daily send caps, so for a busier site a dedicated transactional provider is the steadier choice.
Which is the best free SMTP provider for WordPress?
There's no single winner, but I reach for Brevo most often: the free tier is generous, setup is quick, and it authenticates cleanly with SPF and DKIM. SendGrid, Mailgun and Amazon SES are solid too. Pick one, add its DNS records, and delivery becomes reliable rather than a gamble.
Which port should I use — 587 (TLS) or 465 (SSL)?
Use port 587 with TLS in almost every case — it's the modern submission port and rarely blocked by hosts. Port 465 with SSL still works and is fine if your provider recommends it. Whichever you pick, the module fills the port in from the provider preset (Elastic Email's preset uses 2525, for instance), so you rarely set it by hand.
Why are my emails still going to spam even after setting up SMTP?
Usually it's the From address. If it doesn't match the domain you authenticated with SPF and DKIM, inbox providers distrust it. Make sure each relay's From Email is an address on your own domain — never a free Gmail or Yahoo one — and double-check that your DNS records are actually published and correct.
What happens if my email provider goes down?
With a single SMTP plugin, your mail simply fails. The SMTP Mailer module lets you configure multiple relays in priority order, so if the primary one is down, over quota or rejects the login, it automatically retries through the next. If every relay refuses an email, an encrypted copy can be retried up to 5 times within 72 hours (password-reset emails are not kept), and you can be alerted by email or a Slack, Discord or Teams webhook when a send fails (at most one alert every 15 minutes).
Is there a monthly sending limit on free SMTP tiers?
Yes. Free tiers all cap you — Brevo allows a few hundred emails a day, others meter by the month. For transactional mail like password resets and form notifications that's usually plenty. If you send newsletters or run a busy store, watch the quota, or configure a fallback relay to catch the overflow.
Comments